Code Agency

#security

13 articles tagged security.

16 min read

Headless commerce with Odoo and React: the complete guide

Decouple the storefront from Odoo and you get a faster, safer, upgrade-proof shop. DragonflyDB caching, island architecture, GitHub version control, PR previews, VPN-isolated ERP, PWA mobile UX — everything we ship on every headless e-commerce project.

odooreactecommerceheadlessnextjsperformancesecuritypwacaching
16 min read

Expired, then deleted: the credential dates nobody is watching

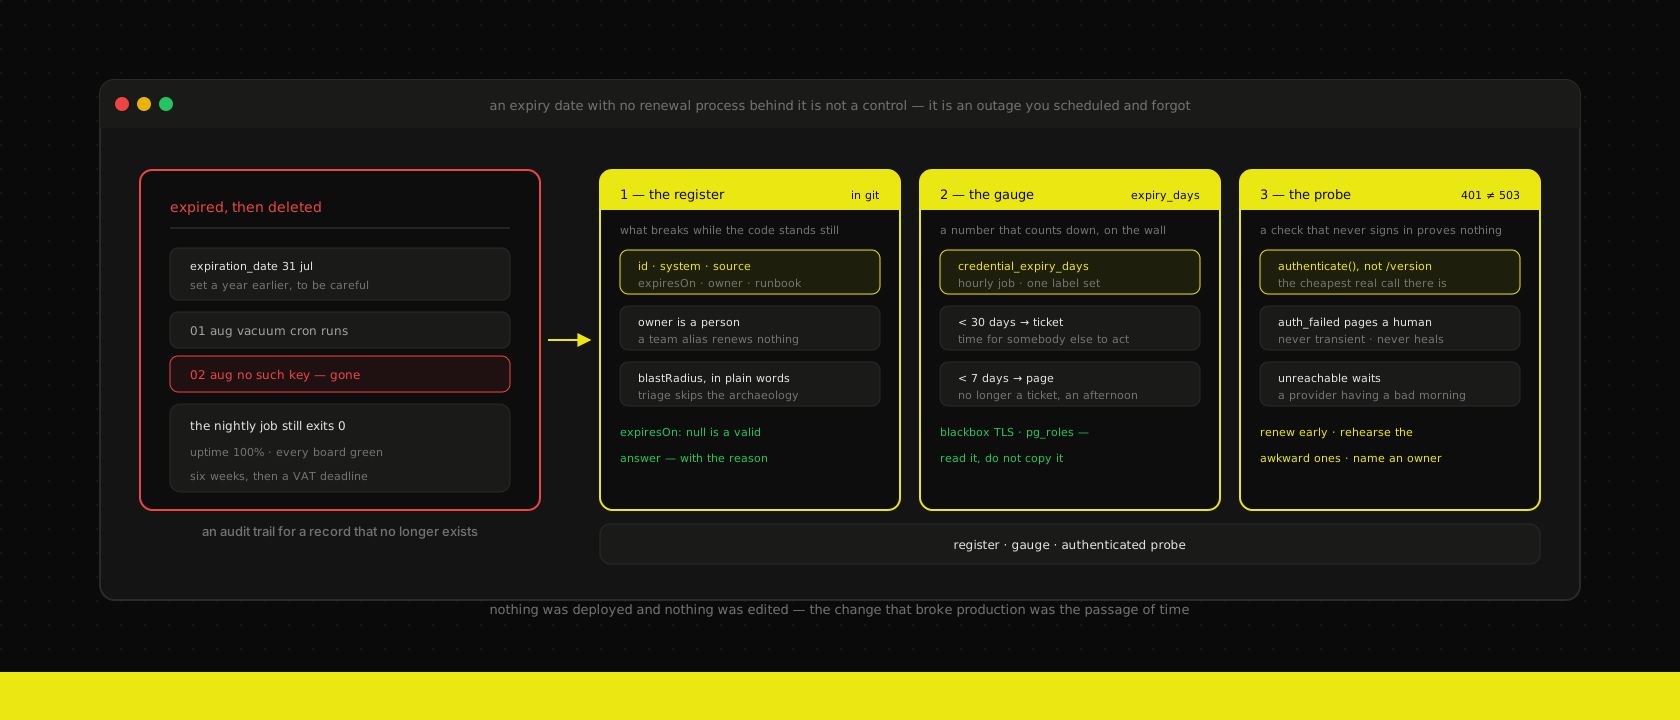
A nightly export ran green for six weeks while sending nothing, because the API key it used had an expiration date on it and a housekeeping cron deleted the record the day after it lapsed. The three ways a credential dies, why only one of them is loud, and the register, the gauge and the authenticated probe that turn a surprise outage into a calendar entry.

devopssecuritymonitoringobservabilityodoo
13 min read

Most of a Content Security Policy is free. The rest costs you static rendering.

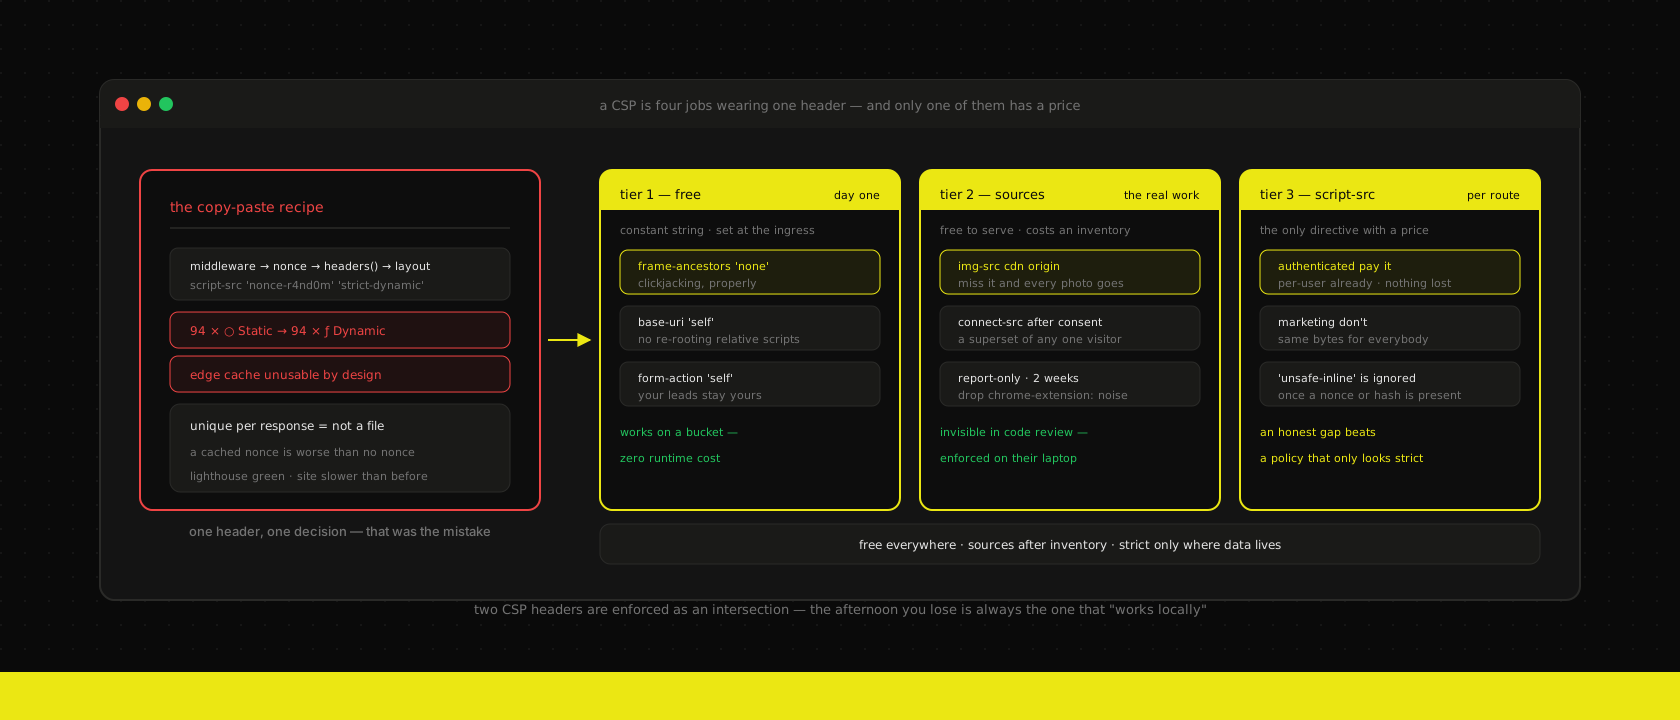
A security questionnaire asks for a CSP, you copy the nonce recipe everyone publishes, and your statically generated site quietly becomes a dynamically rendered one. Which directives cost nothing, why the nonce is the expensive part, and how we split a policy so the security lands where it actually matters.

securitynextjsarchitecturedevopsfrontend
14 min read

The 180 MB scan that killed the pod: user uploads that never touch your app server

Raising the body-size limit is the fix that keeps working right up until it doesn't. Why buffering user files through your application is a dead end, the presigned handshake that replaces it, the checks that still have to happen after the bytes land, and why the ERP should be handed a pointer instead of a payload.

architecturenextjssecurityodoodevops
14 min read

One login for the whole stack: OIDC on the tools you already self-host

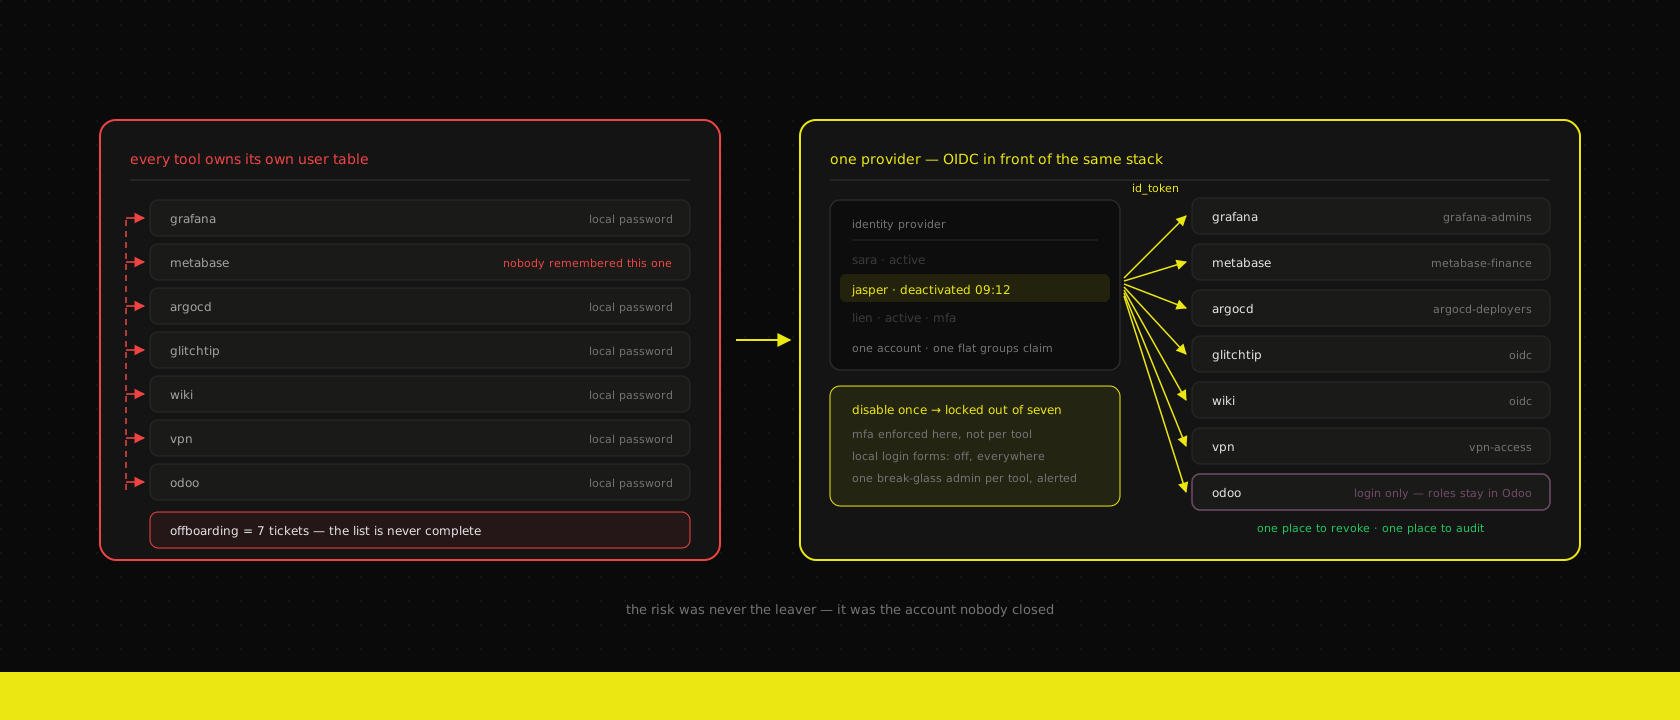
Every self-hosted tool ships its own user table, and a leaver has to be removed from all of them. The identity provider we put in front of Grafana, Metabase, ArgoCD and the custom apps — which parts map cleanly, why Odoo is the awkward one, and what you owe the thing once everything depends on it.

securitydevopskubernetesarchitecture
18 min read

SMS for 2FA: what it's still good for, and what it isn't

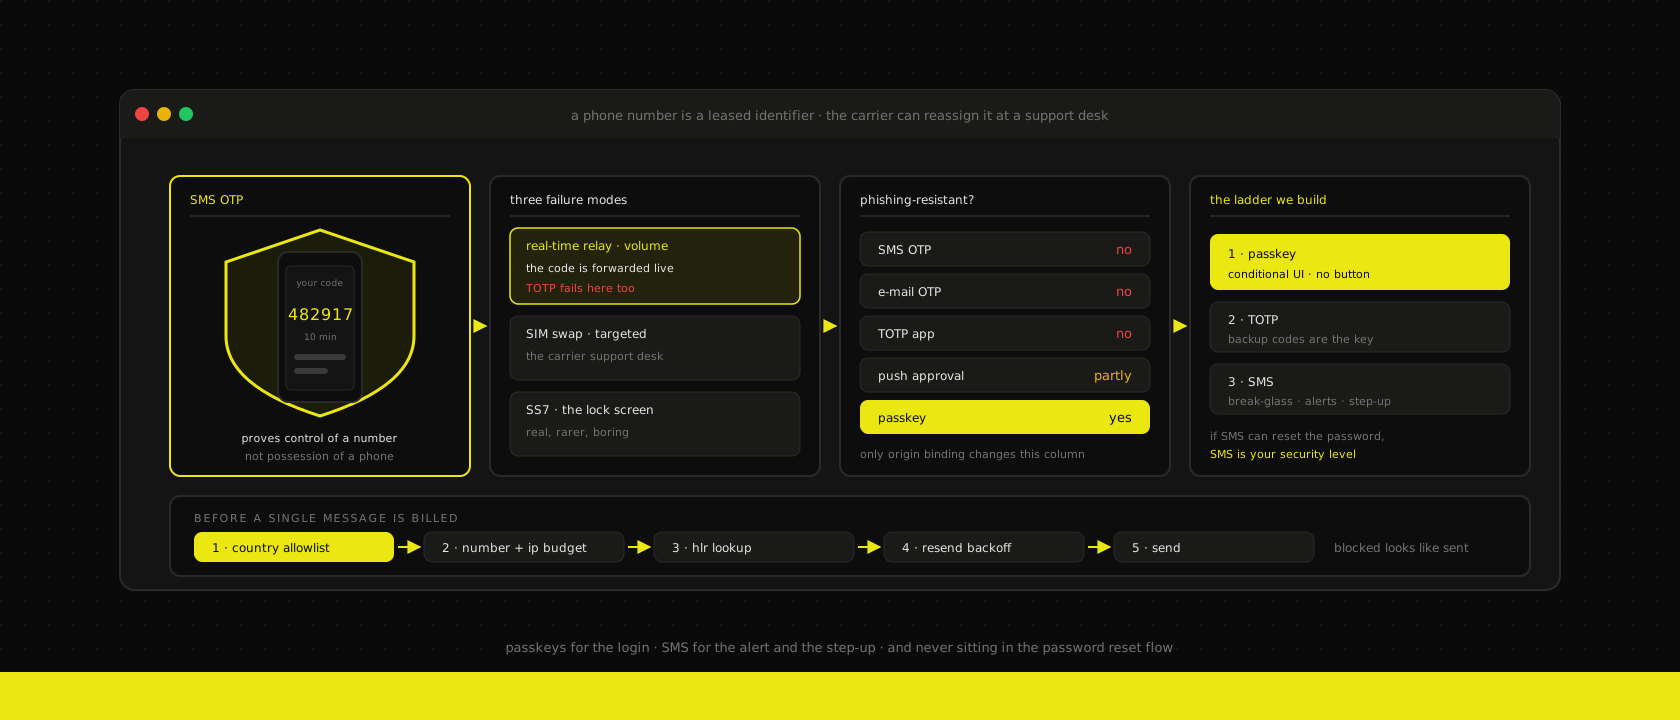
SIM-swap risk is real; so is the customer who will never install an authenticator app. An honest matrix of SMS OTP against TOTP and passkeys — plus the attack that shows up on your invoice instead of your incident channel, the network APIs that turn a phone number back into a useful signal, and why the recovery path decides your real security level, not the login screen.

securitysmsarchitecture
9 min read

Stopping form spam without CAPTCHAs: honeypots, timing and fake success

Making a human prove humanity is a UX tax, and the bots pay it more reliably than your customers do. The invisible gate on every form on this site: a honeypot field, a minimum fill time, and a fake success that teaches the bot nothing — three server-side checks, no third-party script.

securityfrontendnextjs
6 min read

Odoo access rights done right: groups, record rules and the audit trail

Most Odoo installs run with everyone as admin until the first incident. How we design permission groups that mirror the org chart, record rules that hold up under audit, and logging that answers who changed what — before anyone has to ask.

odoosecurityerpaudit