Code Agency

Blog

Articles about software engineering, Odoo, cloud infrastructure and running a digital business.

16 min read

Headless commerce with Odoo and React: the complete guide

Decouple the storefront from Odoo and you get a faster, safer, upgrade-proof shop. DragonflyDB caching, island architecture, GitHub version control, PR previews, VPN-isolated ERP, PWA mobile UX — everything we ship on every headless e-commerce project.

odooreactecommerceheadlessnextjsperformancesecuritypwacaching
16 min read

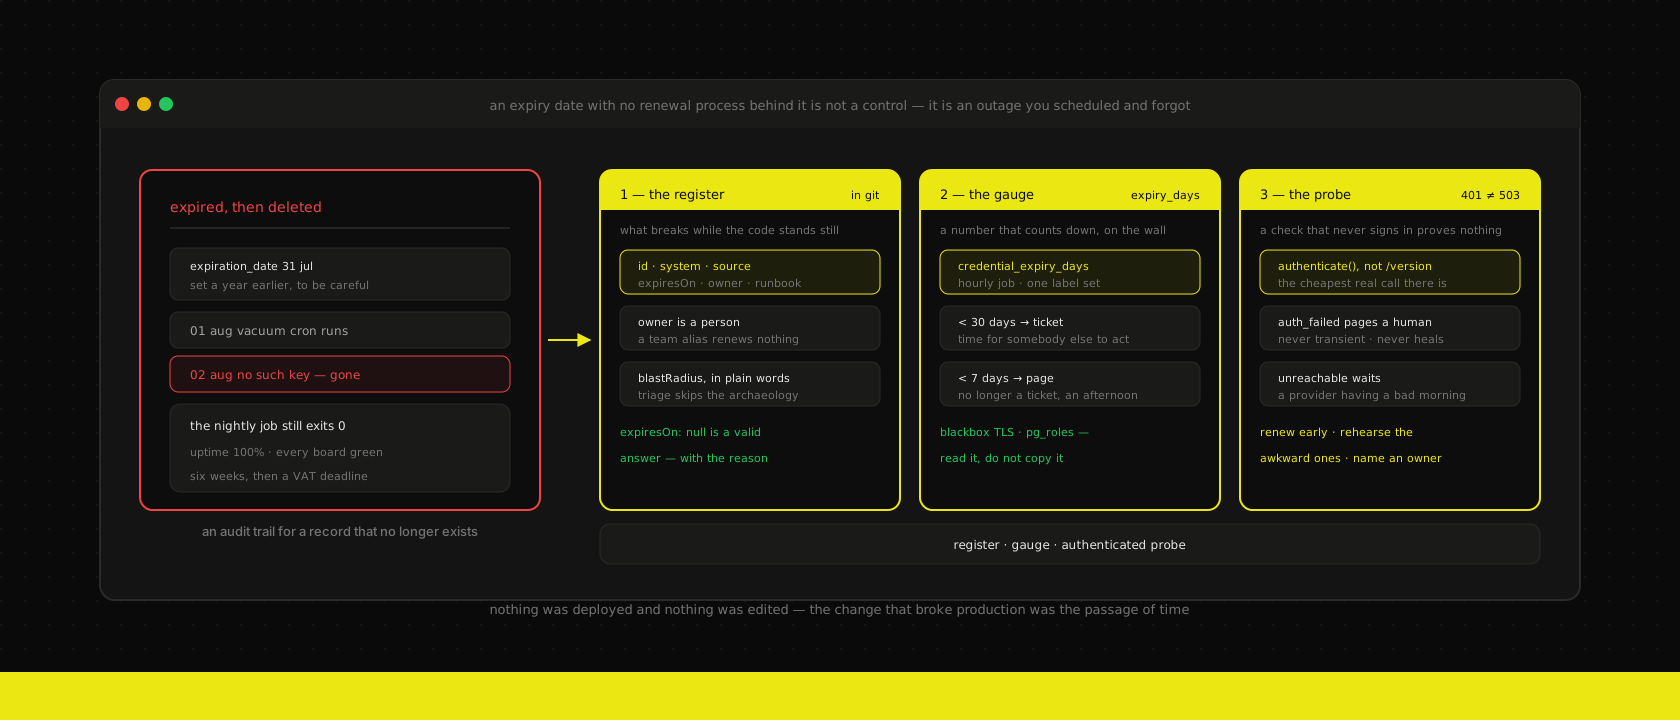
Expired, then deleted: the credential dates nobody is watching

A nightly export ran green for six weeks while sending nothing, because the API key it used had an expiration date on it and a housekeeping cron deleted the record the day after it lapsed. The three ways a credential dies, why only one of them is loud, and the register, the gauge and the authenticated probe that turn a surprise outage into a calendar entry.

devopssecuritymonitoringobservabilityodoo
17 min read

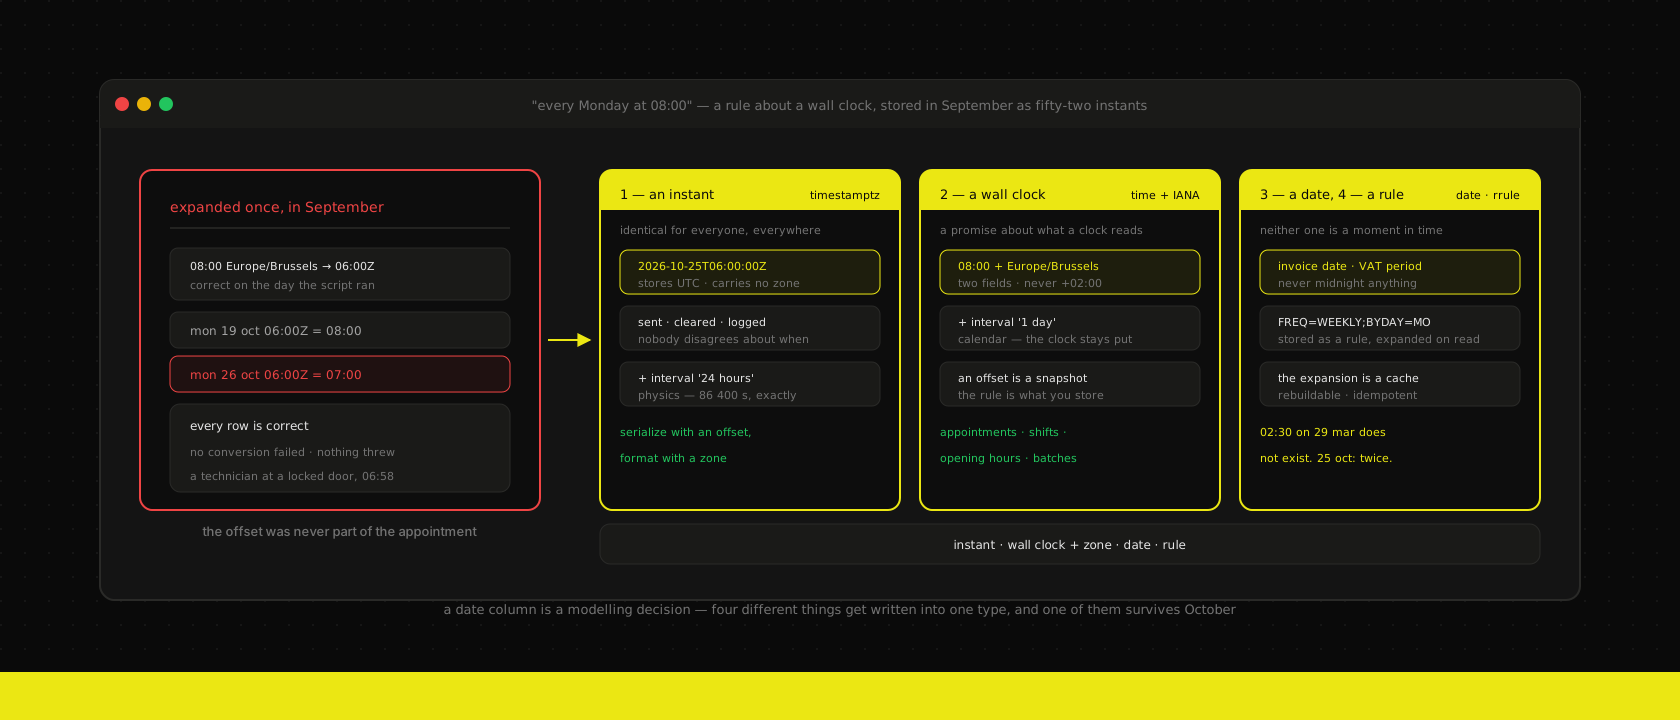
The hour that doesn't exist: time zones, DST and the appointment that moved itself

A technician stood outside a locked building at seven in the morning because a recurring visit had been expanded into absolute instants six weeks before the clocks went back. The three kinds of "when" that don't convert into each other, why a recurrence rule is not a list of timestamps, what Odoo hands you over the API, and how to test a bug that only reproduces twice a year.

architecturepostgresqlodoonextjsdevelopment
13 min read

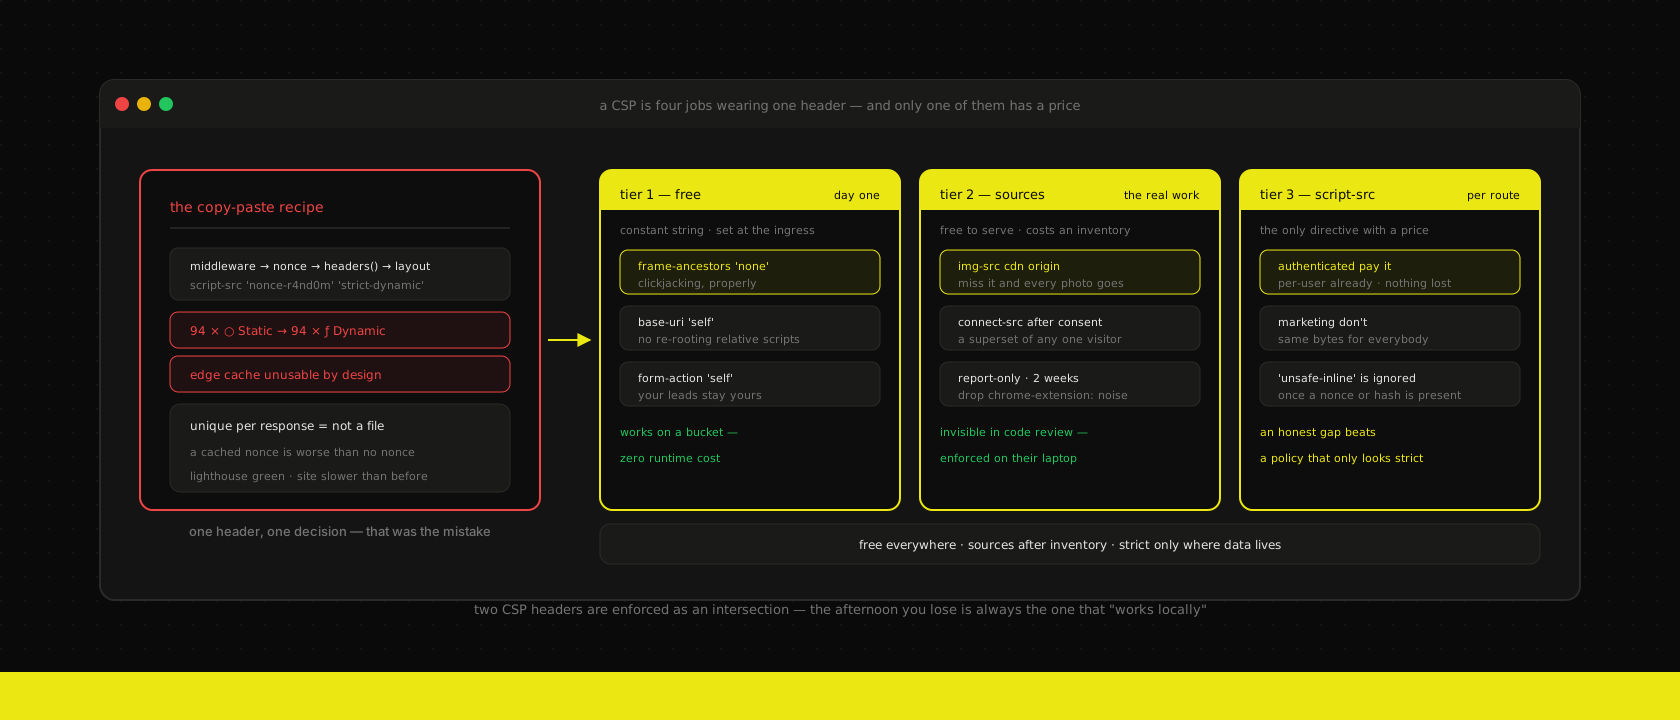
Most of a Content Security Policy is free. The rest costs you static rendering.

A security questionnaire asks for a CSP, you copy the nonce recipe everyone publishes, and your statically generated site quietly becomes a dynamically rendered one. Which directives cost nothing, why the nonce is the expensive part, and how we split a policy so the security lands where it actually matters.

securitynextjsarchitecturedevopsfrontend
14 min read

The 180 MB scan that killed the pod: user uploads that never touch your app server

Raising the body-size limit is the fix that keeps working right up until it doesn't. Why buffering user files through your application is a dead end, the presigned handshake that replaces it, the checks that still have to happen after the bytes land, and why the ERP should be handed a pointer instead of a payload.

architecturenextjssecurityodoodevops
19 min read

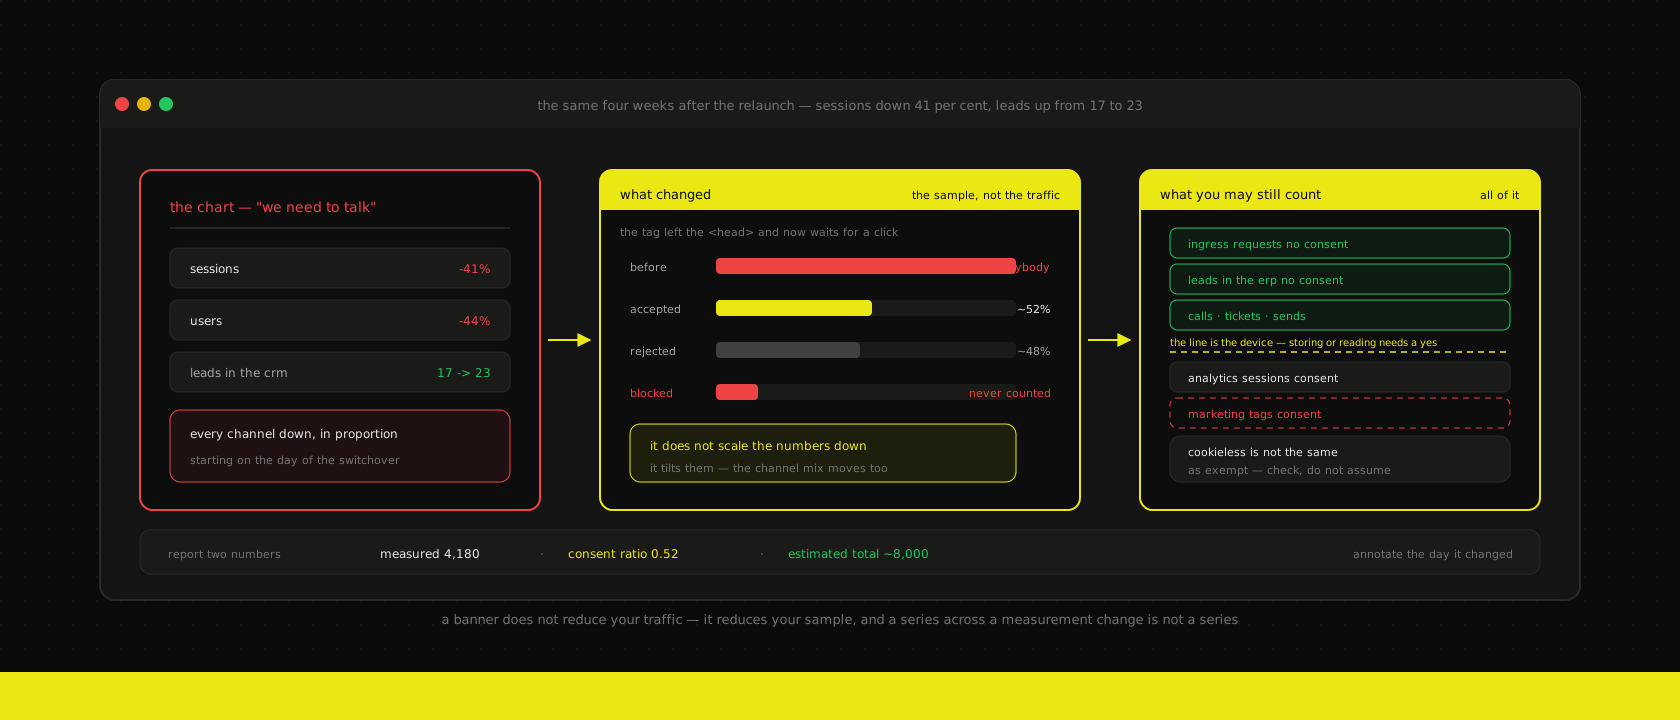
Your traffic didn't drop, your measurement did: analytics after the consent banner

Sessions fell 41% the month after the relaunch and the leads went up, because the old site counted everybody and the new one only counts the people who said yes. What the consent rule actually covers, why cookieless is not automatically banner-free, the server-side denominator that makes the numbers honest again, and why the count that pays lives in the ERP.

marketingbusinessseofrontendnextjs
18 min read

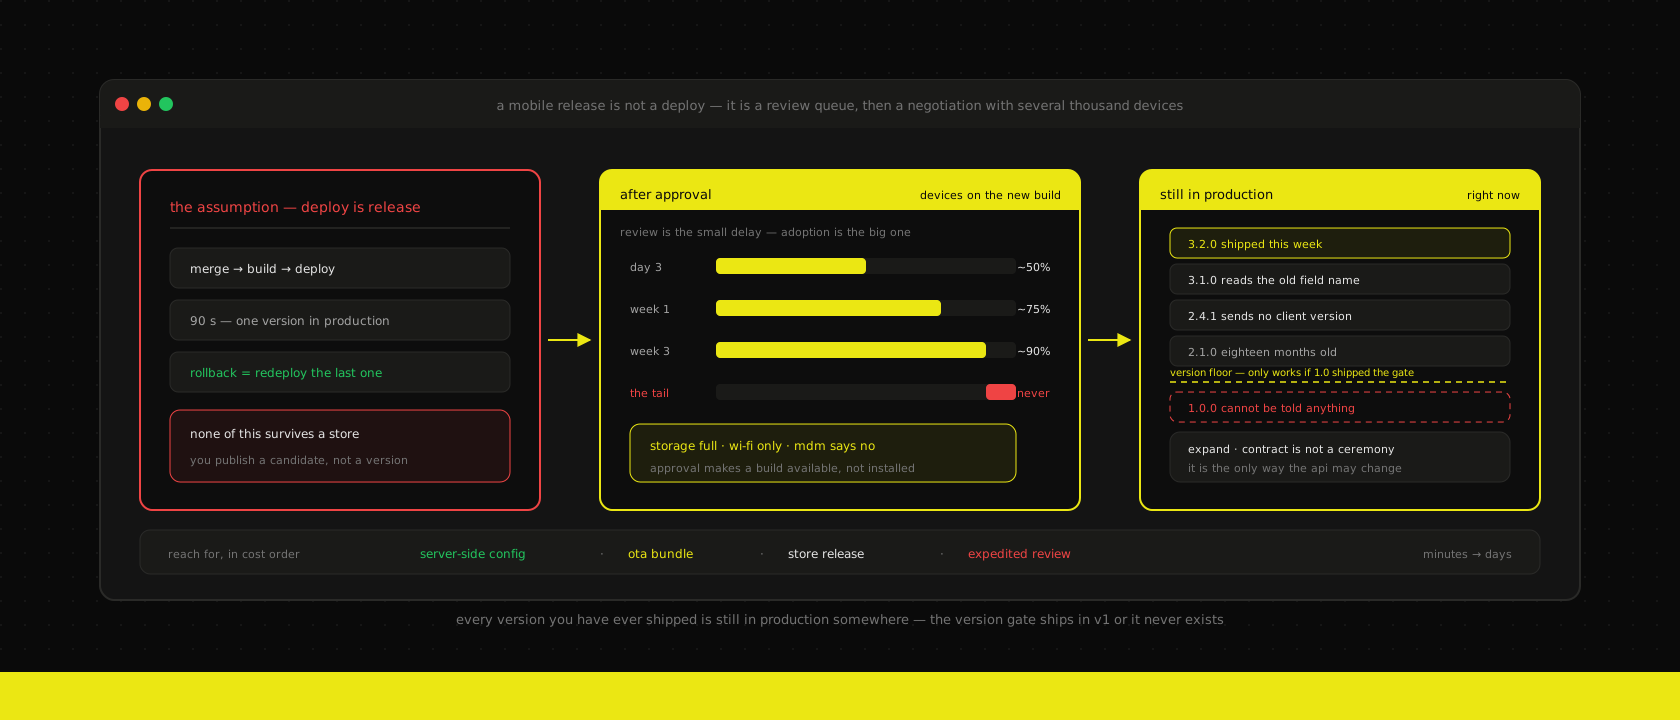
The version you can't take back: releasing a React Native app when the store is in the middle

The fix took forty minutes and a quarter of your users still hit the bug three weeks later, because a mobile release is a copy on somebody else's device. What over-the-air updates genuinely replace, the minimum-version gate you have to ship in v1 or never, why your API is permanently multi-version, and the autumn maintenance window nobody schedules.

mobilereactdevopsarchitectureapi
18 min read

The redirect map is the migration: relaunching a site without losing the traffic

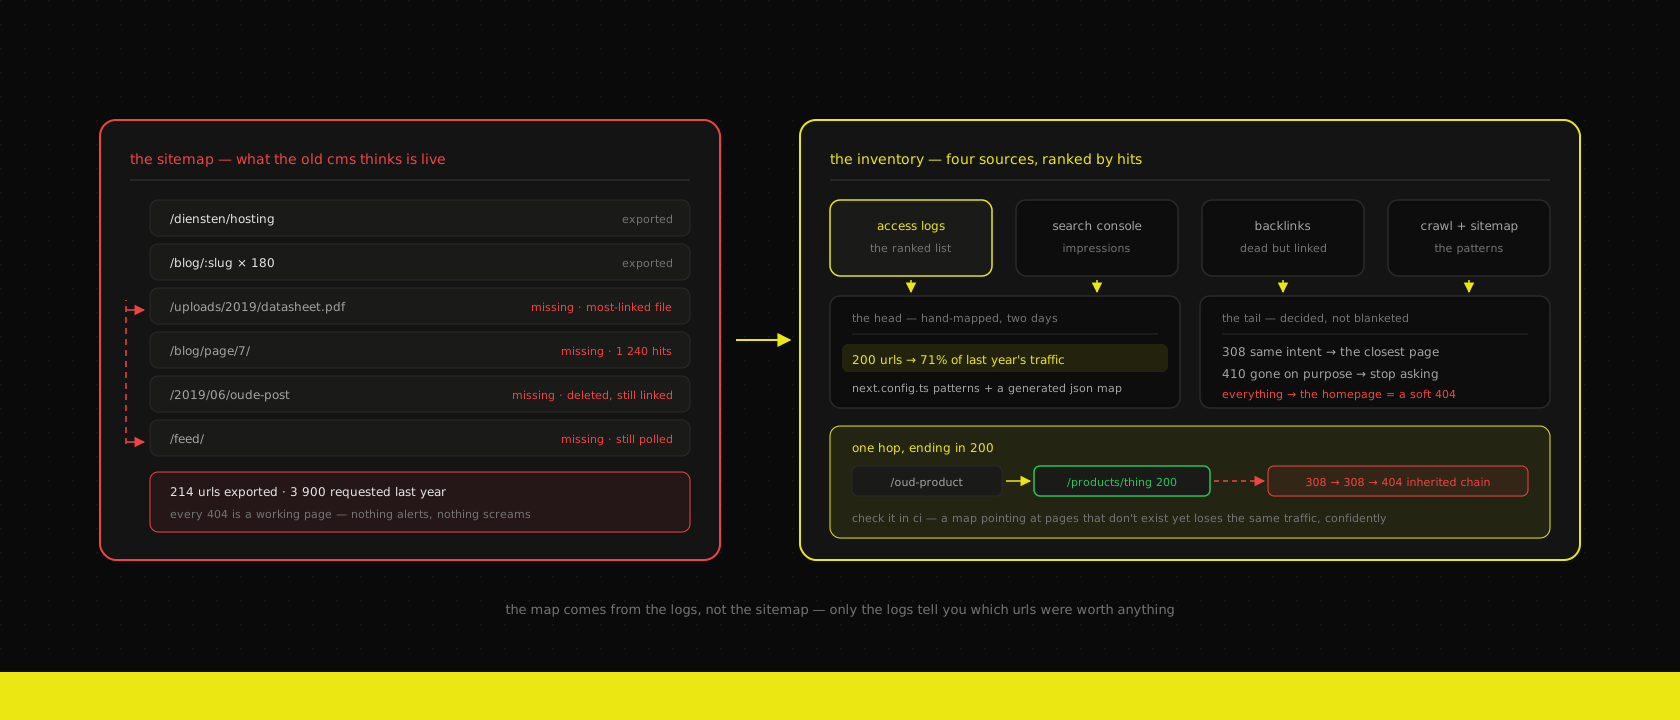
The new site is faster and better looking, and three weeks later organic sessions are down a third. Nothing looks broken, because a 404 is a working page. Where the URL inventory actually comes from, why the sitemap isn't it, where redirects belong in a Next.js stack, and the rule that stops people blanket-redirecting a thousand URLs to the homepage.

seonextjsmigrationwordpressbusiness
18 min read

The PDF stopped being the invoice: eight months of Belgian B2B e-invoicing

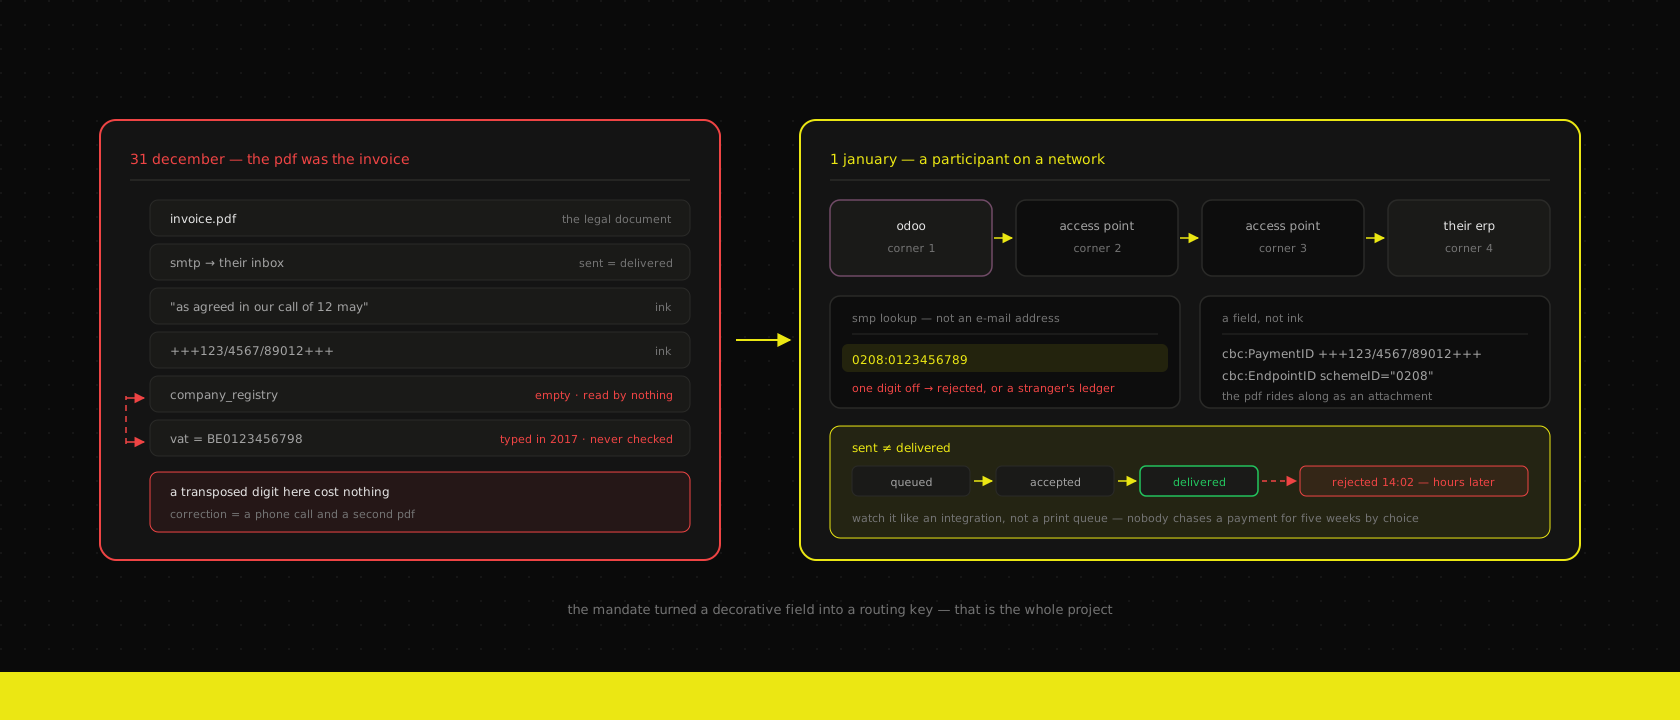
Belgium's structured e-invoicing mandate landed on 1 January. Switching it on was an afternoon; everything it exposed was the quarter that followed. What Peppol actually addresses, why the failures live in your contact records rather than your ERP, what UBL refuses to carry, and why 'sent' stopped meaning 'delivered'.

odooaccountingerpbusinessautomation
19 min read

Who's calling: matching a number to a customer before the phone stops ringing

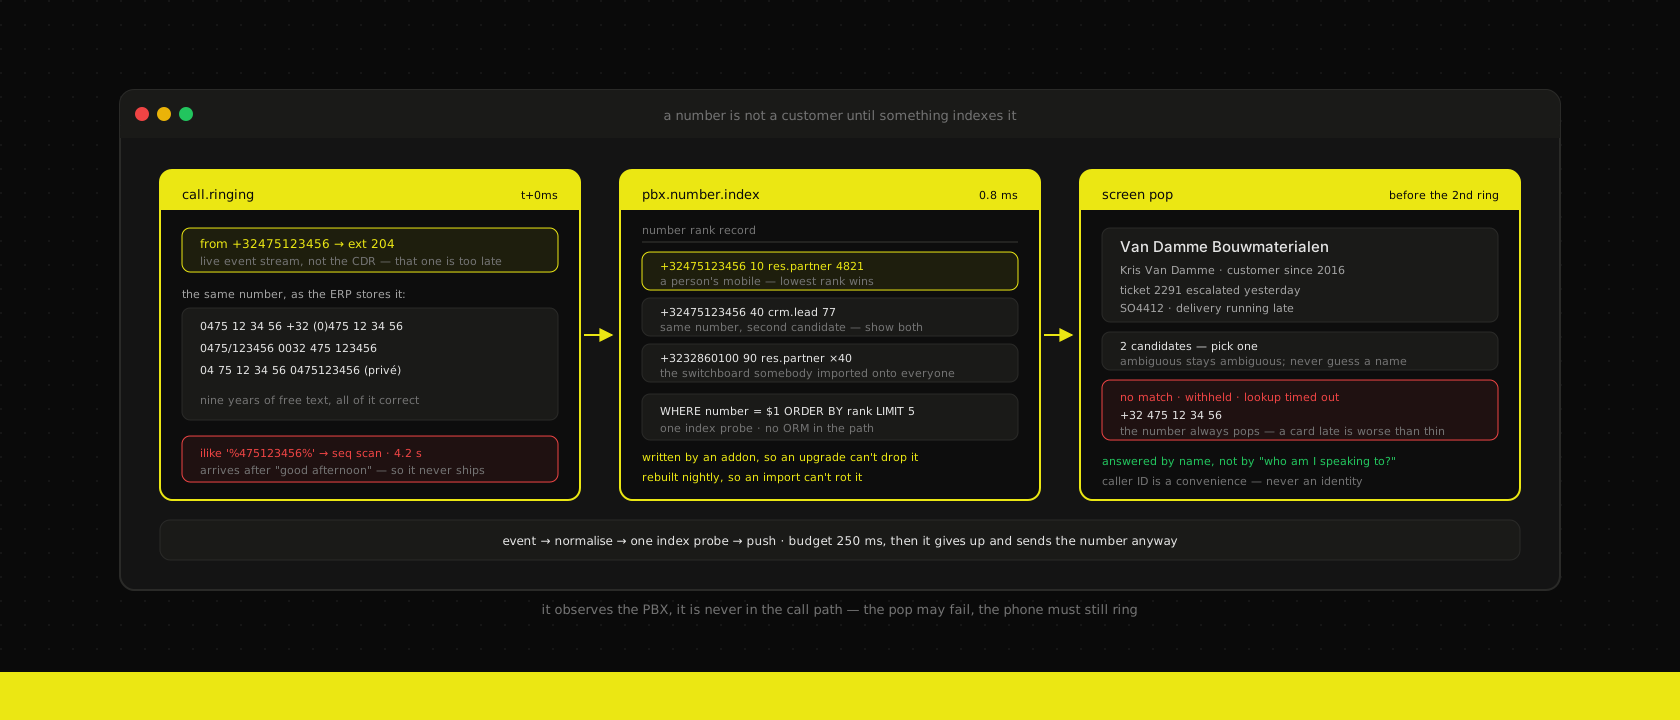
A phone system knows a number. An ERP knows a customer. In most companies nothing knows both, and closing that gap is a harder problem than the vendor demo suggests — nine years of phone numbers nobody normalised, an event stream instead of a polling loop, and a screen pop that must never be able to stop a call.

telephonyodooarchitectureautomationerp
14 min read

One login for the whole stack: OIDC on the tools you already self-host

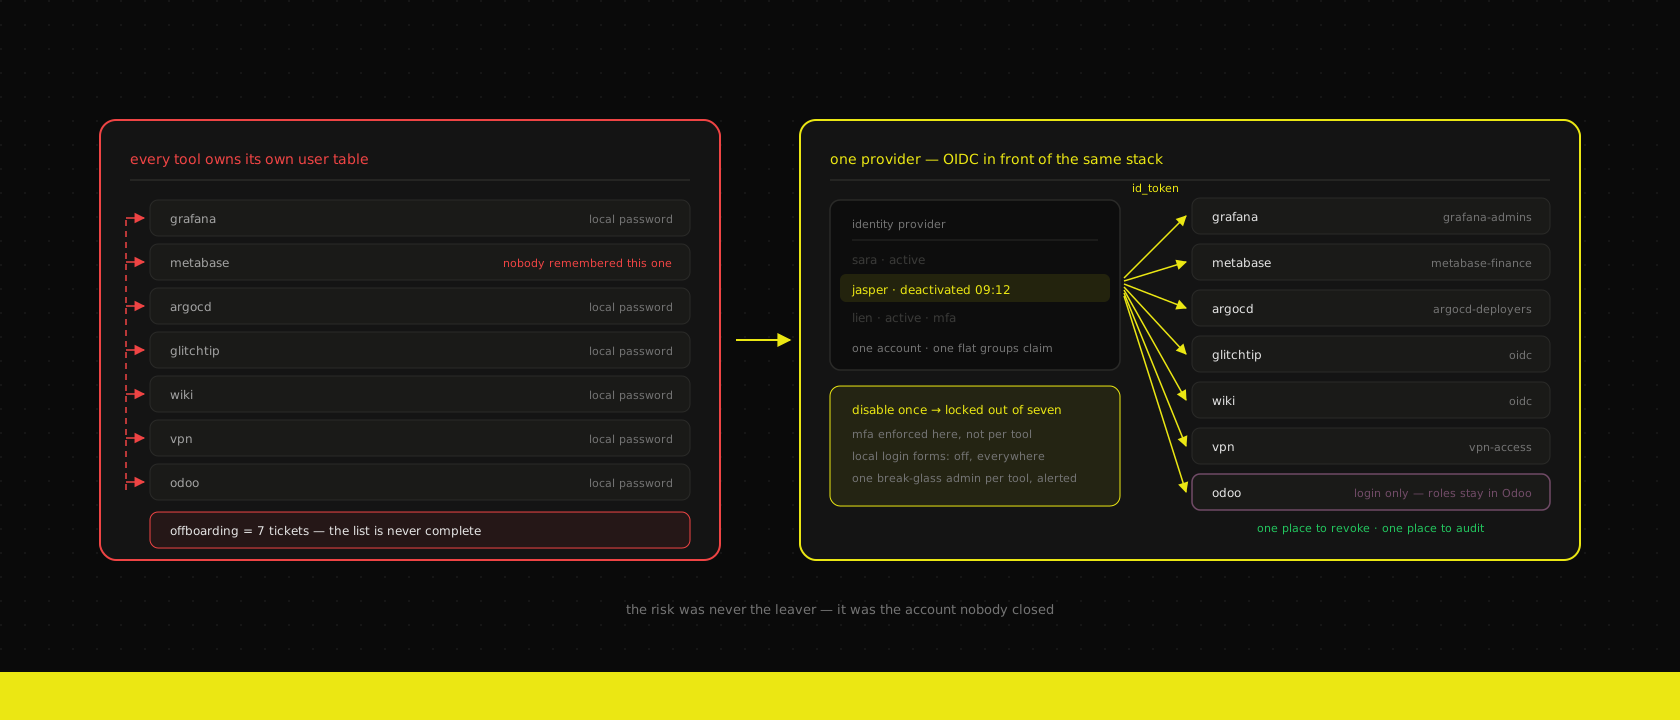
Every self-hosted tool ships its own user table, and a leaver has to be removed from all of them. The identity provider we put in front of Grafana, Metabase, ArgoCD and the custom apps — which parts map cleanly, why Odoo is the awkward one, and what you owe the thing once everything depends on it.

securitydevopskubernetesarchitecture
17 min read

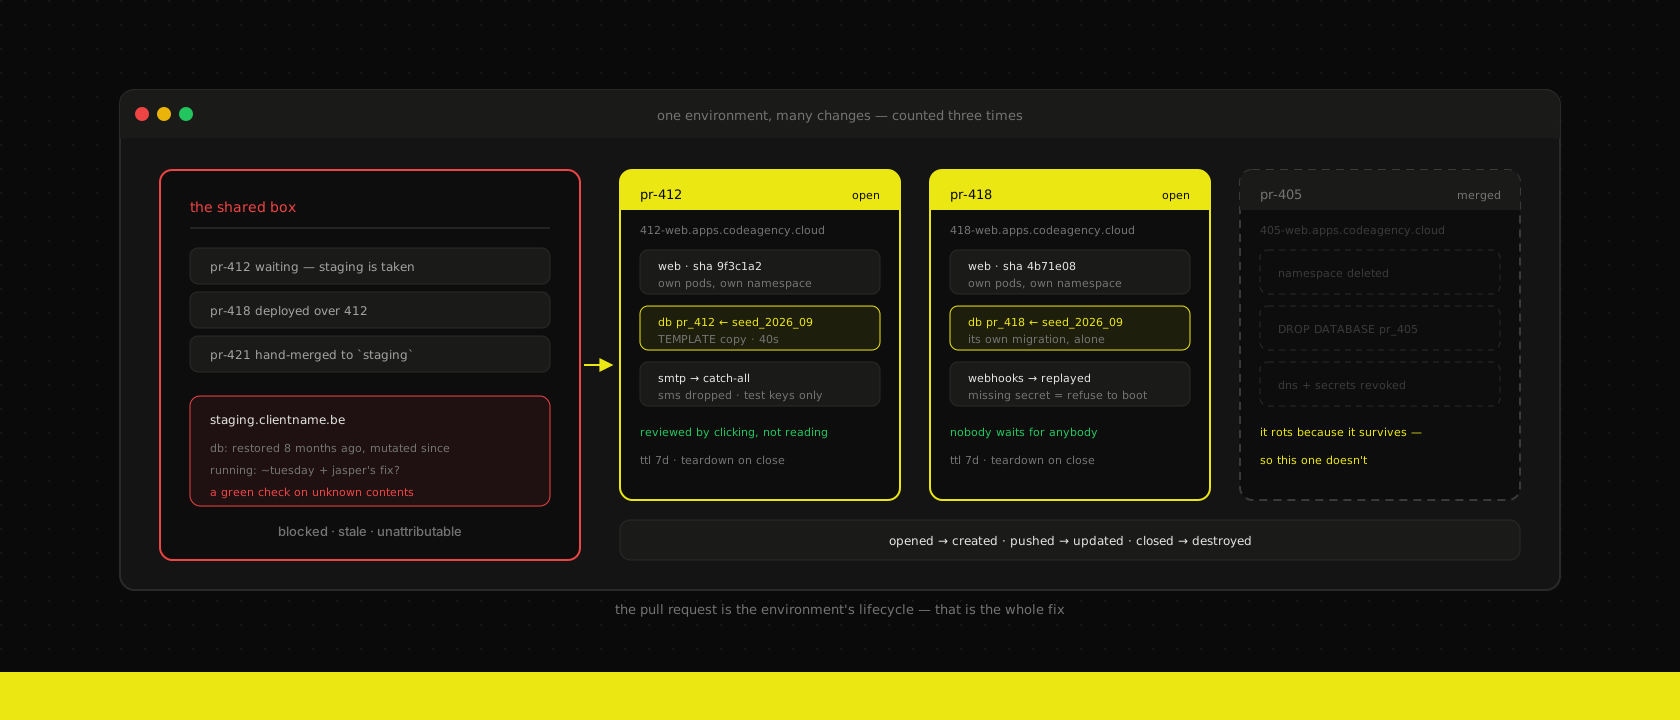
The staging environment lie: why PR previews replaced ours

One shared staging server is always broken, always blocked and always stale — and every fix for that is really a fix for it being shared. What it takes to give each pull request a real environment instead: the database copy, the seed nobody owns, the integrations that must fail closed, and the teardown that is the whole point.

devopskubernetestestinggitops

Want us to publish something specific?

Tell us what you'd like to read and we'll add it to our writing queue.