Code Agency

#devops

26 articles tagged devops.

16 min read

Expired, then deleted: the credential dates nobody is watching

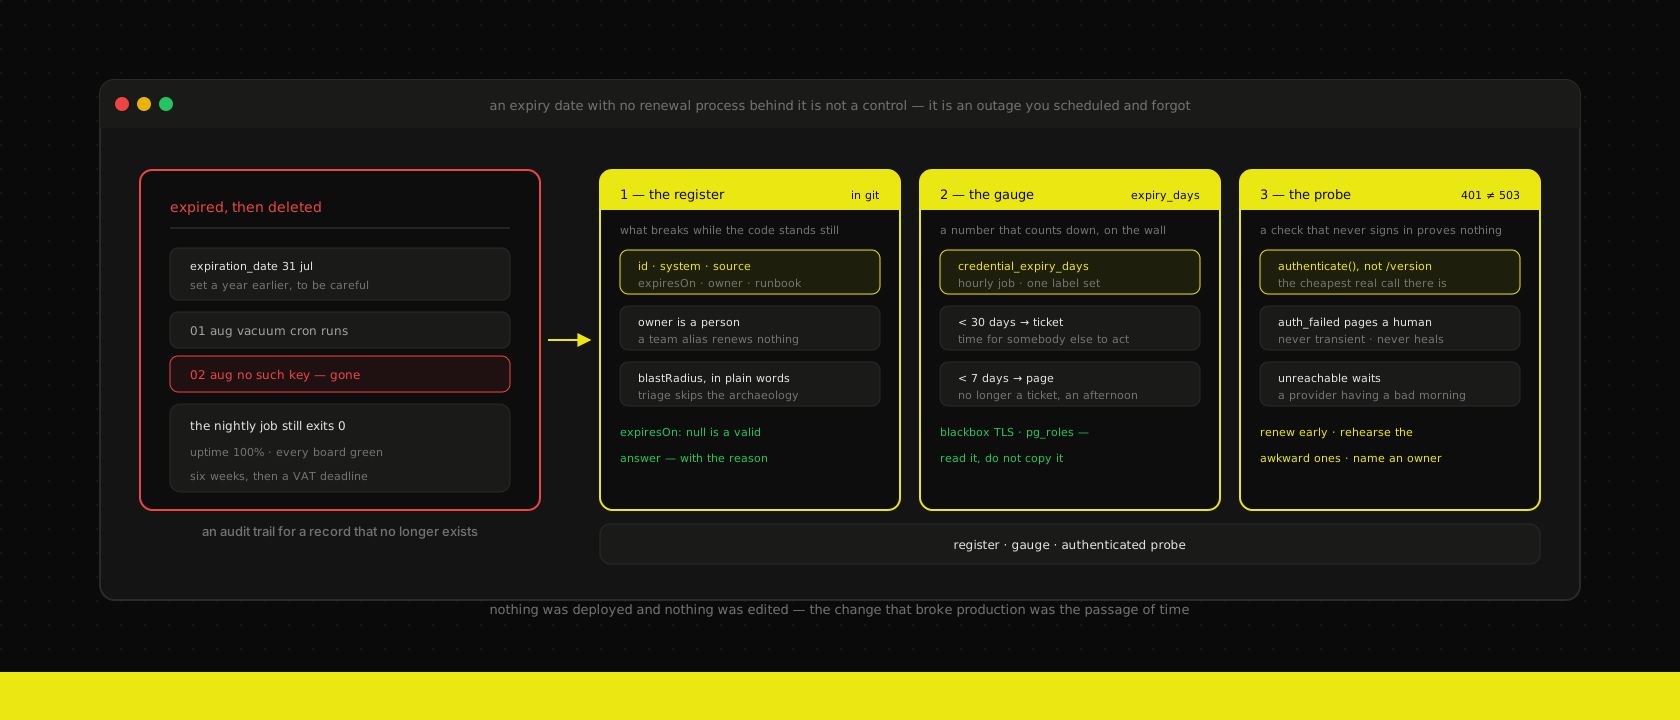
A nightly export ran green for six weeks while sending nothing, because the API key it used had an expiration date on it and a housekeeping cron deleted the record the day after it lapsed. The three ways a credential dies, why only one of them is loud, and the register, the gauge and the authenticated probe that turn a surprise outage into a calendar entry.

devopssecuritymonitoringobservabilityodoo
13 min read

Most of a Content Security Policy is free. The rest costs you static rendering.

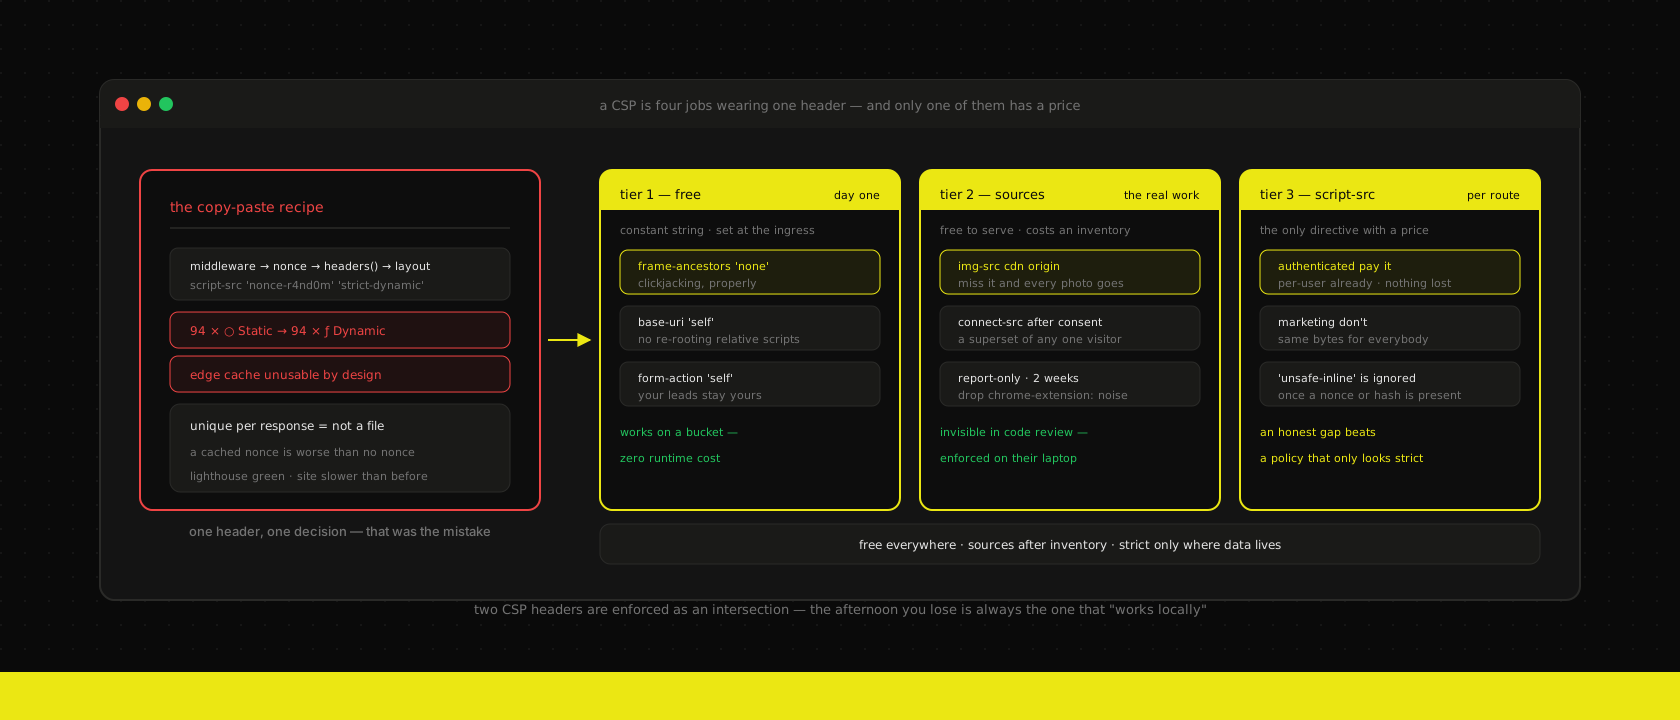
A security questionnaire asks for a CSP, you copy the nonce recipe everyone publishes, and your statically generated site quietly becomes a dynamically rendered one. Which directives cost nothing, why the nonce is the expensive part, and how we split a policy so the security lands where it actually matters.

securitynextjsarchitecturedevopsfrontend
14 min read

The 180 MB scan that killed the pod: user uploads that never touch your app server

Raising the body-size limit is the fix that keeps working right up until it doesn't. Why buffering user files through your application is a dead end, the presigned handshake that replaces it, the checks that still have to happen after the bytes land, and why the ERP should be handed a pointer instead of a payload.

architecturenextjssecurityodoodevops
18 min read

The version you can't take back: releasing a React Native app when the store is in the middle

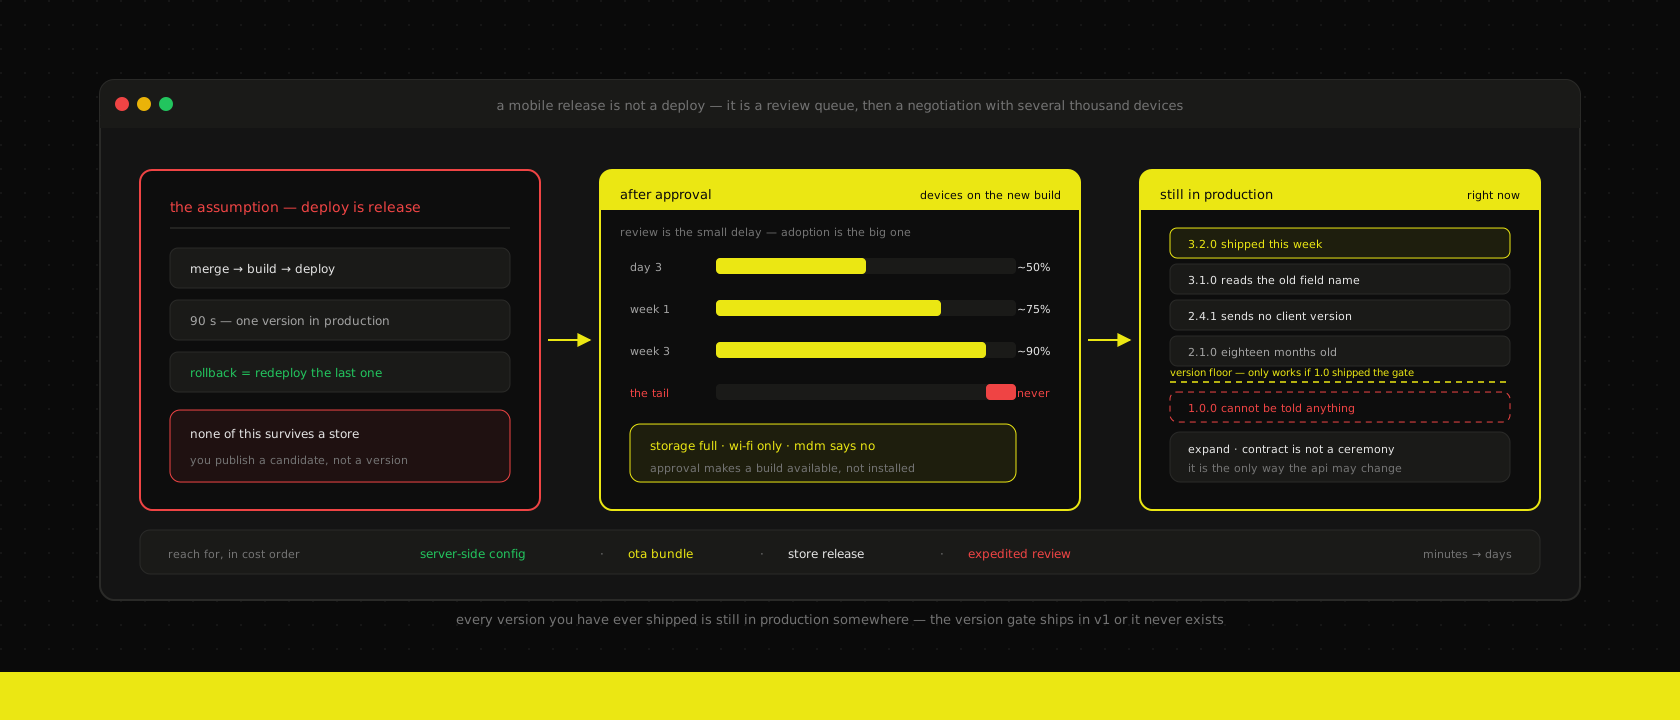
The fix took forty minutes and a quarter of your users still hit the bug three weeks later, because a mobile release is a copy on somebody else's device. What over-the-air updates genuinely replace, the minimum-version gate you have to ship in v1 or never, why your API is permanently multi-version, and the autumn maintenance window nobody schedules.

mobilereactdevopsarchitectureapi
14 min read

One login for the whole stack: OIDC on the tools you already self-host

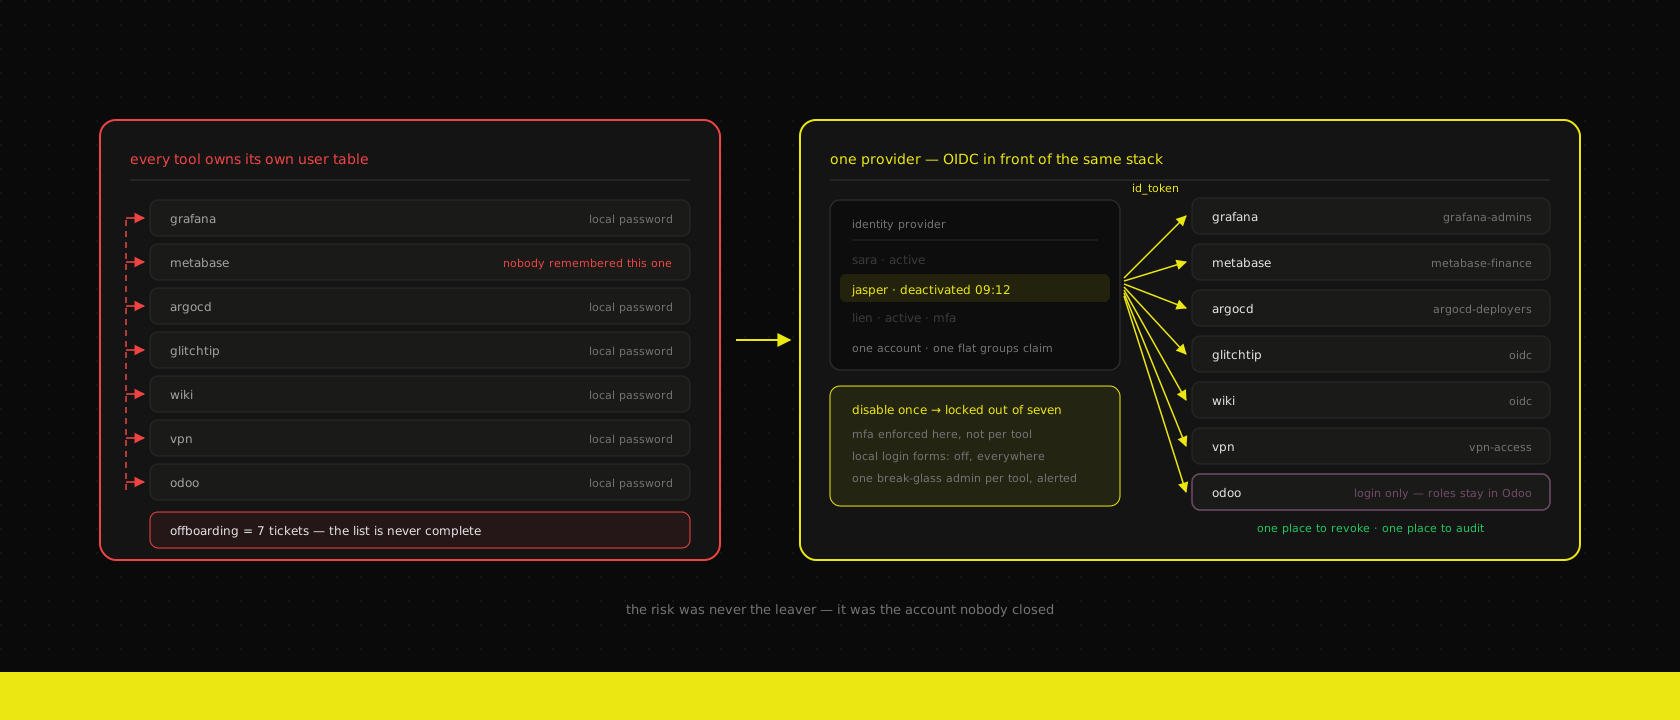
Every self-hosted tool ships its own user table, and a leaver has to be removed from all of them. The identity provider we put in front of Grafana, Metabase, ArgoCD and the custom apps — which parts map cleanly, why Odoo is the awkward one, and what you owe the thing once everything depends on it.

securitydevopskubernetesarchitecture
17 min read

The staging environment lie: why PR previews replaced ours

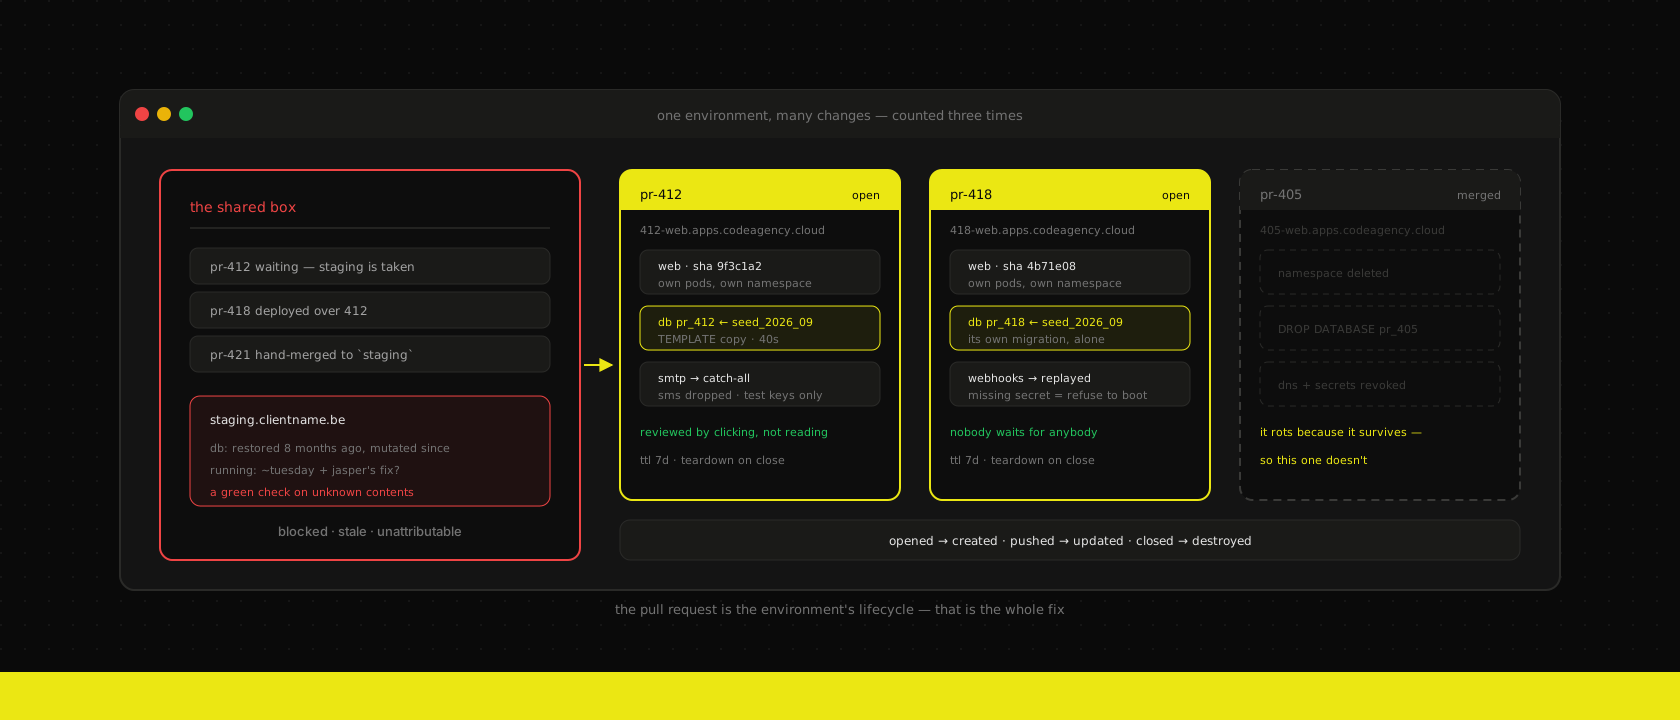
One shared staging server is always broken, always blocked and always stale — and every fix for that is really a fix for it being shared. What it takes to give each pull request a real environment instead: the database copy, the seed nobody owns, the integrations that must fail closed, and the teardown that is the whole point.

devopskubernetestestinggitops
16 min read

The column you can't just rename: schema changes without a maintenance window

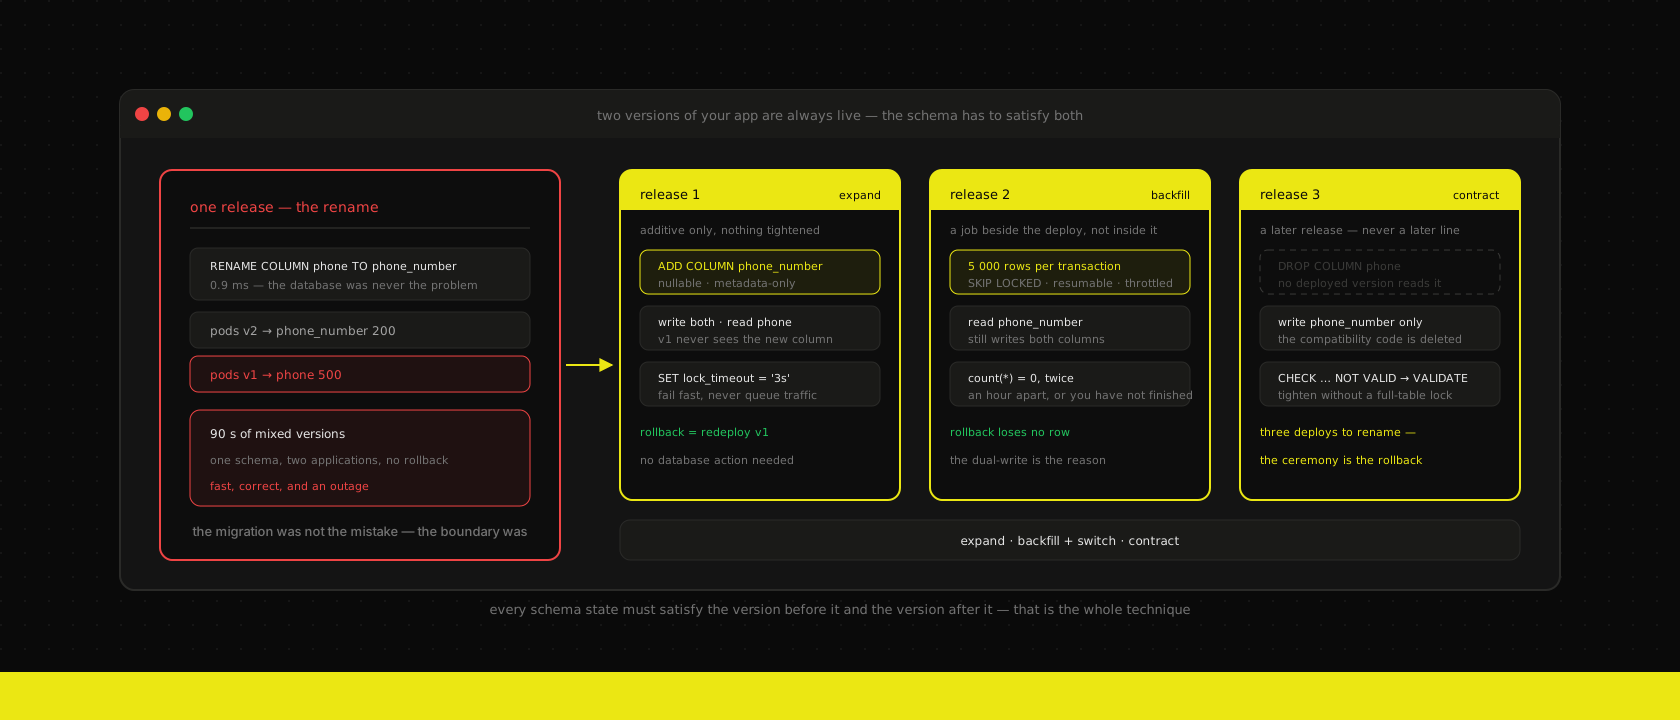
A rename is the cheapest thing a database does and one of the most dangerous things a deploy does, because two versions of your application are always live at once. Expand, backfill, contract — the release boundary that makes it safe, the locks that bite anyway, and what changes when Odoo owns the schema.

postgresqldevopsarchitectureodoodevelopment
18 min read

The stale screen problem: offline-first signage that fails loudly

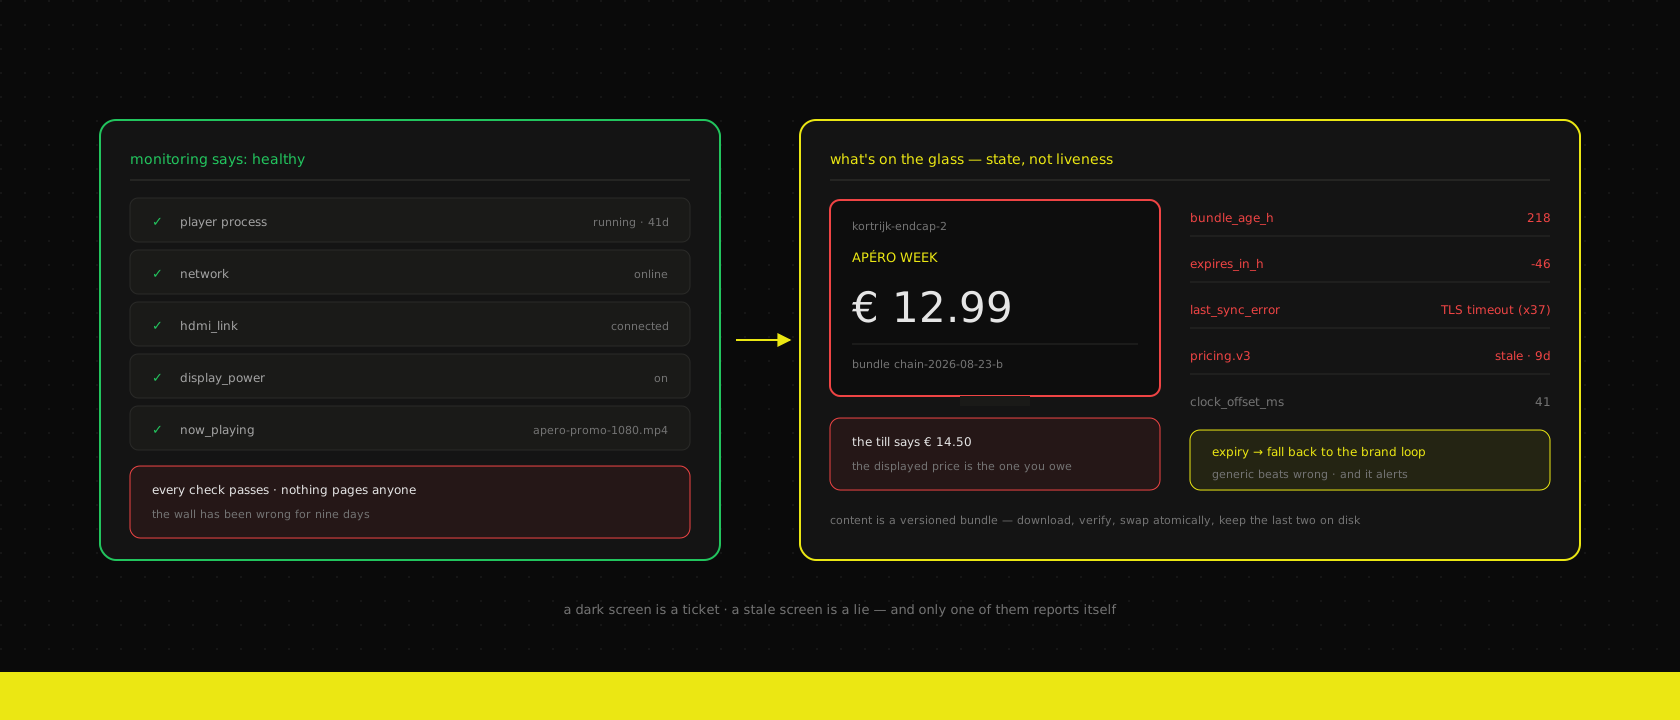
A dark screen is a support ticket. A screen still showing last week's price is a lie in your store, and nothing in a normal monitoring stack will tell you about it. Content as a versioned bundle instead of a URL, day-parts that depend on a clock you don't control, expiry as a safety feature, and telemetry that reports what's actually on the glass.

signagearchitecturedevopsmonitoring
15 min read

What a care plan should contain: maintenance contracts worth signing

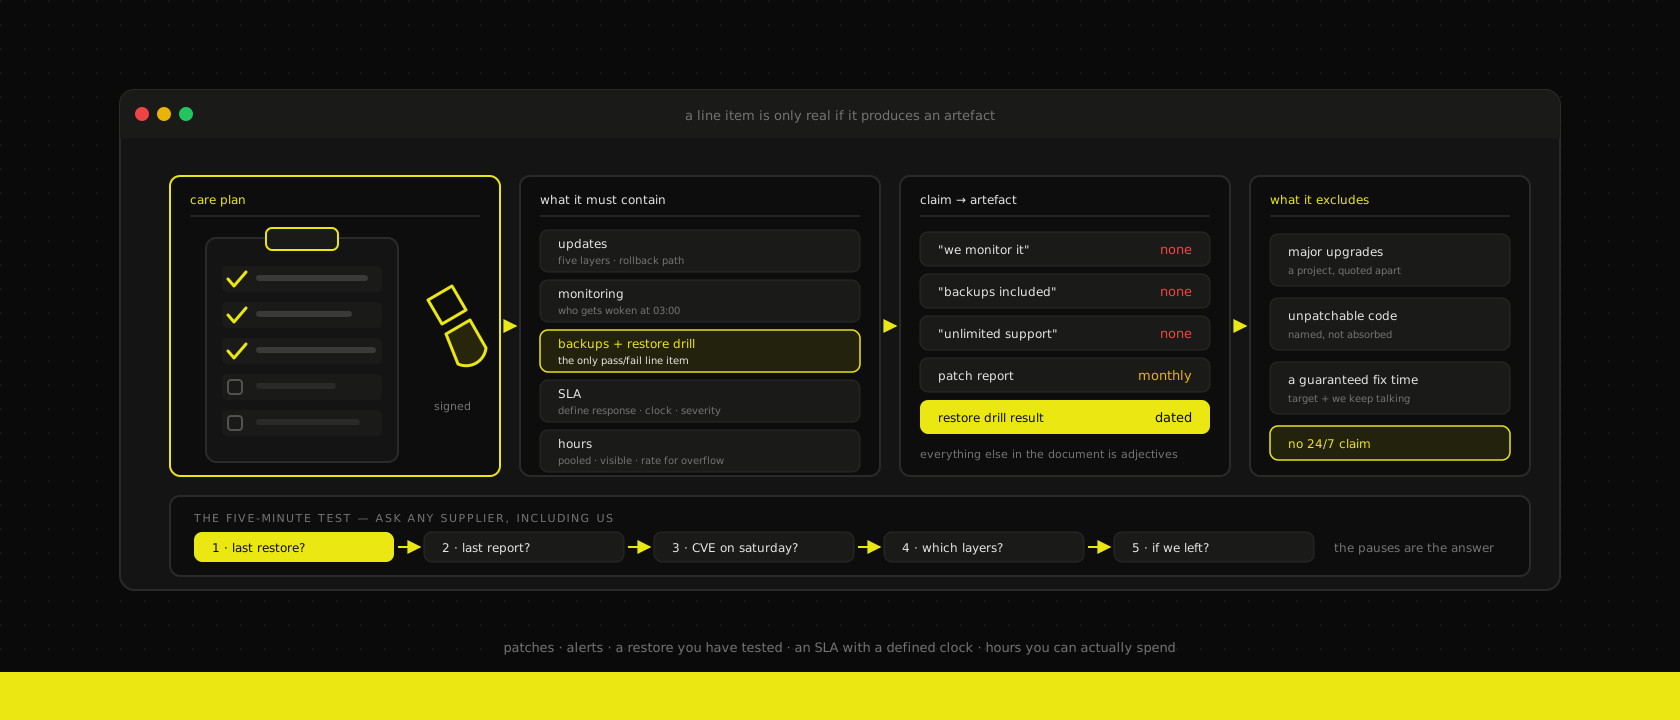
Most maintenance contracts are a monthly invoice with a promise attached. The line items that make one real — patch cadence, backups you have restored, an SLA that says what a clock is and when it runs, and hours you can actually spend — plus the questions that expose a hollow one in five minutes, applied to ours as well as everyone else's.

businessmaintenancedevops
9 min read

Media on the CDN, code on the origin: a delivery strategy that ages well

Next.js will happily serve your JS bundles from a CDN with one config line. We stopped doing that. Hashed chunks belong to the build that emitted them; images outlive every deploy — and treating both as 'assets' is how a rollback turns into a cache-purge incident.

performancearchitecturedevopsnextjs
4 min read

Restore drills: the monthly ritual that makes backups real

A backup nobody has restored is a hypothesis, not a plan. The monthly drill we run against Velero snapshots, Postgres dumps and filestore syncs — and what it's already caught before a client ever noticed.

kubernetesdevopsbackupsdisaster-recovery
6 min read

CloudNativePG in production: Postgres on Kubernetes without fear

Four years running CloudNativePG under ERPs and web apps: declarative failover, WAL-archived backups and major-version upgrades as config, not 3 AM SSH sessions. The gotchas to plan for, and where we'd still reach for something else.

postgresqlkubernetesdevops
6 min read

Your AI assistant has amnesia: adding a memory layer with mem0

Every session starts from zero: the same stack briefing, the same corrections, the same tokens burned re-explaining decisions you made months ago. mem0 gives AI development a persistent memory — what it actually does, the numbers behind it, and why we self-host it on our own cluster.

aidevelopmentdevops